Enterprise AI becomes more useful when it can see the customer, commercial and operational context behind a task. But connecting that context creates a new management problem: the business must decide what data can be reached, which actions are permitted and where the authoritative record remains.
The temptation is to solve integration by copying everything into one new repository. That can speed up a pilot, but it also multiplies data, access rules, retention duties and reconciliation work. A more durable model treats connected context as a governed service rather than another data migration.
Context is valuable only when it is current
A seller preparing for a meeting may need pipeline status, recent purchases, service history, documents and financial signals. An assistant that sees only part of that picture can produce confident but incomplete advice. The problem is not merely model quality; it is the freshness and coverage of the context supplied to the model.
Leaders should therefore separate two questions. First, can the system retrieve the information required for the task? Second, can it prove where that information came from and when it was last updated? Without lineage and timestamps, more context can create more uncertainty.
Zero-copy is an operating principle, not a slogan
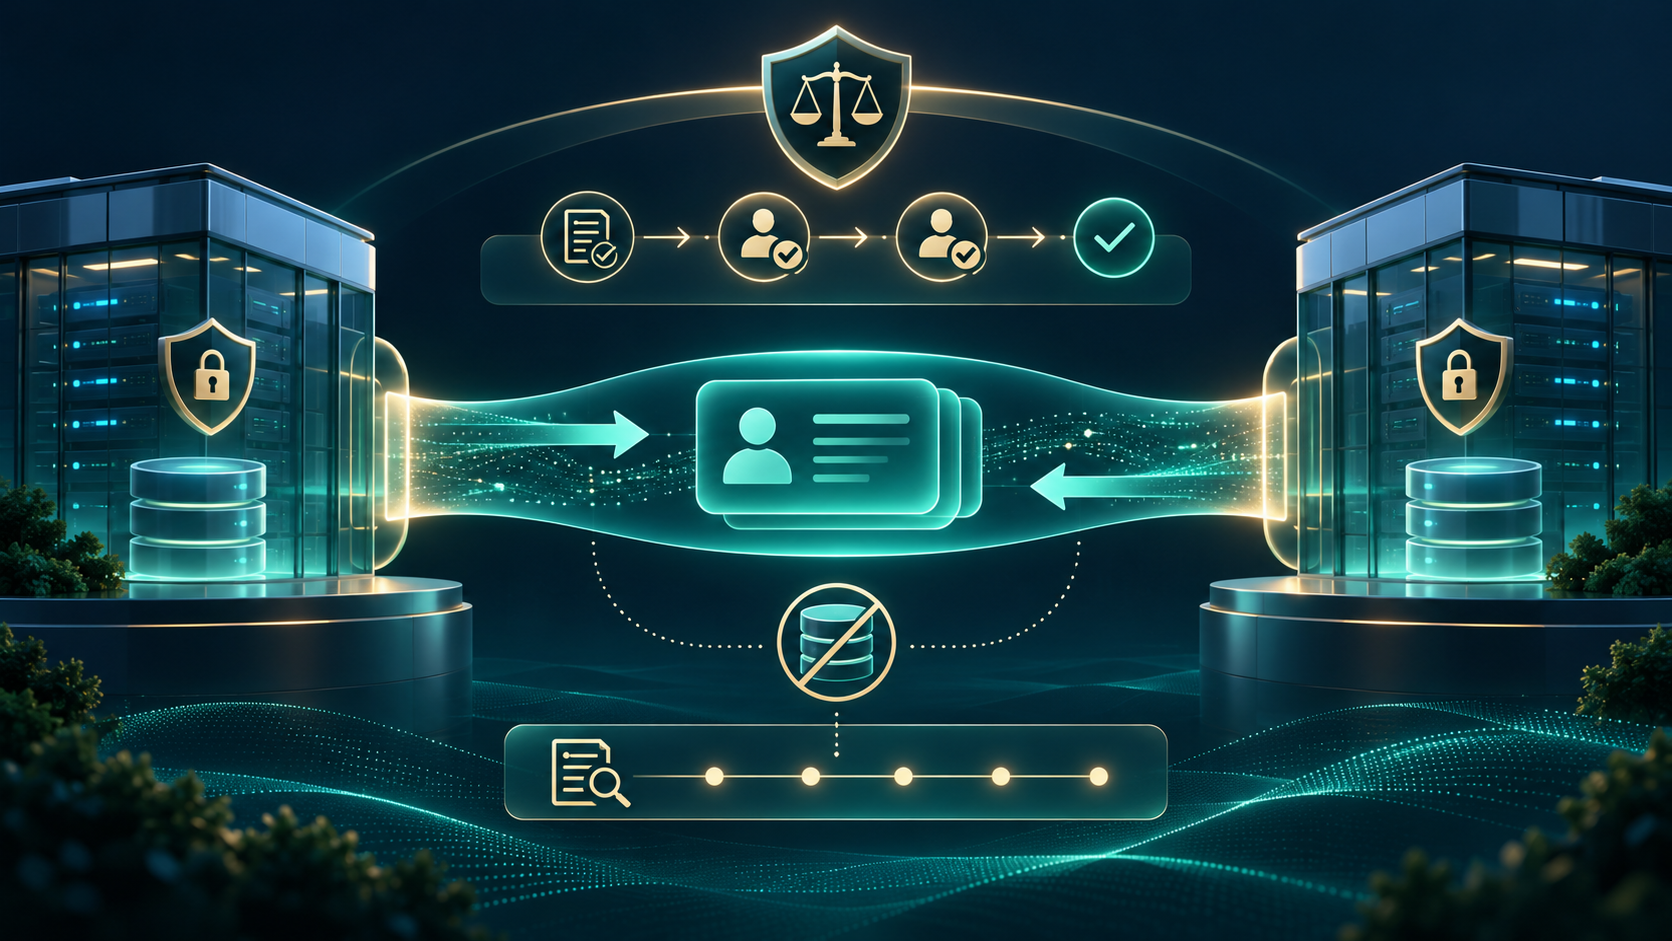
Direct access across governed systems can reduce the need to build and maintain duplicate data pipelines. That does not mean data never moves at a technical level. It means the business avoids creating another uncontrolled master copy merely to make a workflow possible.
The practical benefits are fewer reconciliation jobs, less duplicated storage and a clearer source of truth. The trade-off is greater dependence on identity, permissions, availability and query performance across system boundaries. A zero-copy architecture needs stronger operational controls, not fewer controls.
Read access and action authority are different
An AI assistant may be allowed to summarize a customer account without being allowed to change it. It may draft a follow-up message but require a person to approve sending. It may recommend an opportunity-stage update while leaving the final writeback to an accountable employee.
This distinction should be explicit in the permission architecture. Each tool or action needs a defined scope, an owner and an approval rule. Treating all access as one broad permission makes it difficult to contain mistakes and nearly impossible to explain who authorized a consequential change.
Keep the source system authoritative
When customer context appears inside collaboration tools, analytics environments or AI interfaces, users may assume the visible copy is the record. The operating model should state clearly which system owns each field and which interfaces are views, caches or derived summaries.
Writeback needs the same clarity. If a user approves a change from an AI interface, the transaction should still pass the validation rules of the authoritative system. The interface should not become a shortcut around data quality, mandatory fields or compliance checks.
Design for least privilege and task boundaries
Broad access may make demonstrations impressive, but production systems should expose only the data and actions required for a defined task. A service agent may need purchase and support history but not payroll data. A sales assistant may need account activity but not unrestricted export rights.
Task boundaries also improve evaluation. Teams can test whether a workflow retrieved the right records, respected permissions and proposed an appropriate action. Vague enterprise-wide knowledge access is harder to secure and harder to measure.
Make confirmation visible
Human approval is useful only when the reviewer can understand what will happen. A confirmation step should identify the destination record, the fields that will change, the proposed values and any downstream effects. A generic approval button shifts responsibility to the user without giving them enough information to exercise it.
High-risk actions may require a second reviewer, a cooling-off period or a narrower set of permitted values. The control should match the consequence, not the novelty of the technology.
Build an audit trail that answers business questions
Technical logs often record that an API call occurred, but business governance needs more. It should be possible to reconstruct which user initiated the task, what context the system retrieved, which model or workflow proposed the action, what the person approved and whether the destination accepted the change.
This record supports incident review, compliance and process improvement. It also helps separate a model error from stale source data, an incorrect permission or a failed integration.
Measure the duplication you avoid
The business case for connected context should include more than assistant usage. Useful measures include the number of duplicate datasets retired, reconciliation jobs eliminated, permission exceptions reduced, time saved in preparing customer interactions and the share of actions completed without a data-quality correction.
Cost and risk can move in opposite directions. Avoiding a large data copy may reduce storage and pipeline work while increasing dependence on real-time connections. The architecture decision should make both sides visible.
Start with one governed customer journey
A sensible first deployment is a journey with clear data ownership and a small set of reversible actions, such as preparing an account briefing and drafting a follow-up. Define the authoritative systems, permission checks, approval points, failure states and evidence required to close the task.
Once that workflow is reliable, the organization can expand access and action scope deliberately. The strategic advantage does not come from connecting every system at once. It comes from making customer context useful without losing control of the record.